Cloud & DevOps
Pass the security reviewbefore the customerasks
Security assessments, hardening, identity and access controls, and compliance readiness aligned to ISO 27001, SOC 2 and GDPR — built into how your systems run, with evidence generated as you operate.
- Risk first
- Real exposures prioritised and fixed before the questionnaire arrives.
- Evidence as you operate
- Controls automated and logged so audits are a matter of sharing, not scrambling.
- Framework-aligned
- Controls mapped to ISO 27001, SOC 2 and GDPR requirements.
- 8–12 weeks
- From assessment to audit-ready posture.
- 3
- Frameworks supported
Overview
Most security work stalls becauseit starts with a questionnaire
Enterprise deals slow down when a long security questionnaire arrives and nobody can answer it with evidence. We assess your real risks first — applications, cloud configuration, identity, data handling — and fix the ones that matter most.
Controls are automated and documented as they are built, so the next audit or customer review is a matter of sharing evidence rather than scrambling for it. Where a formal certification is the goal, we prepare the environment and evidence and work alongside your chosen auditor.
Who this is for
- Product companies facing their first enterprise security questionnaire
- Organisations preparing for ISO 27001 or SOC 2 with a chosen auditor
- IT leaders who need a prioritised, honest view of exposure across cloud and applications
- 20+
- Security assessments completed
- 8–12 weeks
- From assessment to audit readiness
What's included
What you get from thisengagement
Working software and a documented reason for each decision — not a slide deck of possibilities.
Security assessment
A prioritised review of applications, cloud configuration, identity and access, and data handling — ranked by real risk.
Hardening
Fixes for the highest risks first — patching, encryption, network rules, secrets management and configuration baselines.
Compliance readiness
Policies, controls and evidence mapped to ISO 27001, SOC 2 or GDPR requirements, prepared for your auditor.
Identity & access
Single sign-on, MFA and least-privilege roles across your tools and infrastructure, with access reviews.
Threat monitoring
Centralised logging and alerting that surface suspicious activity before it becomes an incident.
Incident readiness
Response plans, roles and rehearsals so your team knows exactly what to do on a bad day.
Our approach
From exposure toevidence, in threephases
Each phase ends with something you can review and a decision point where you can stop.
Start with an assessment- Application, cloud and access review
- Gap analysis against your target framework
- Risk-ranked findings with remediation plan
- Fixed-scope estimate
You end up with: A prioritised risk register and remediation roadmap with a number.
- Critical and high findings remediated first
- Identity, logging and secrets controls implemented as code where possible
- Policies and procedures written to match how you actually operate
- Evidence collection automated
You end up with: A hardened environment with controls, policies and evidence in place.
- Continuous monitoring and periodic access reviews
- Audit support alongside your certification body
- Vulnerability management and re-assessment cadence
- Handover to your security owner
You end up with: A security posture you can evidence on demand — to customers and auditors.
Not sure which service you actually need?
Describe the problem in thirty minutes and a solution architect will tell you — including when the answer is that you do not need us for this.
Tools we use
Security tools we rely on
Cloud-native controls and widely adopted open tooling.
Identity
- SSO/SAML/OIDC
- MFA
- Cloud IAM
Scanning
- Dependency and container scanning
- SAST
Logging & monitoring
- Centralised logging
- Cloud-native alerting
Infrastructure
- AWS
- Azure
- Terraform
- Kubernetespolicies

Why us
Why partner with Kaidova on security
We build and operate multi-tenant platforms that hold customer data. Security is part of how we engineer, not a separate practice bolted on.
Risk before checklist
We fix what an attacker would actually exploit before we format a policy document.
Engineers, not only auditors
Findings are remediated by people who can change the code and infrastructure, not just report on it.
Evidence by design
Controls are automated so proof exists as a by-product of operating.
Honest about certification
We prepare you for ISO 27001 or SOC 2 and work with your auditor; we do not claim to certify you.
Built to be handed over
Policies, runbooks and monitoring your team can own.
Our work
Results from systems in production
How disciplined engineering translates into operational outcomes. Every figure shown is measured on a live system and approved by the client.
View all case studies 01LieferfairMarketplaces & Logistics
Rebuilding a delivery marketplace to survive its own growth
A fast-growing delivery platform was hitting the limits of its original architecture. We re-engineered the core system for scale, reliability and real-time operations.
Read case study3.2×
Increase in order throughput
 02Construction contractor (on Oplyra)Construction & Trading
One ledger for a contractor running six disconnected systems
Read case study40%
Less time closing the month
 03FastestVPNConsumer Software
Scaling a consumer VPN to millions of sessions a day
Read case study99.9%
Uptime across regions
Related insights
More on security and compliance
Oplyra ERP 3.0: AI estimation and variation orders
How we cut construction estimation time by nearly two thirds.
Read more
Why we build on Odoo instead of reselling it
The commission model quietly distorts platform advice. Here is our alternative.
Read more
Kaidova opens Middle East delivery desk
Live overlap for GCC clients, staffed by the same senior team.
Read more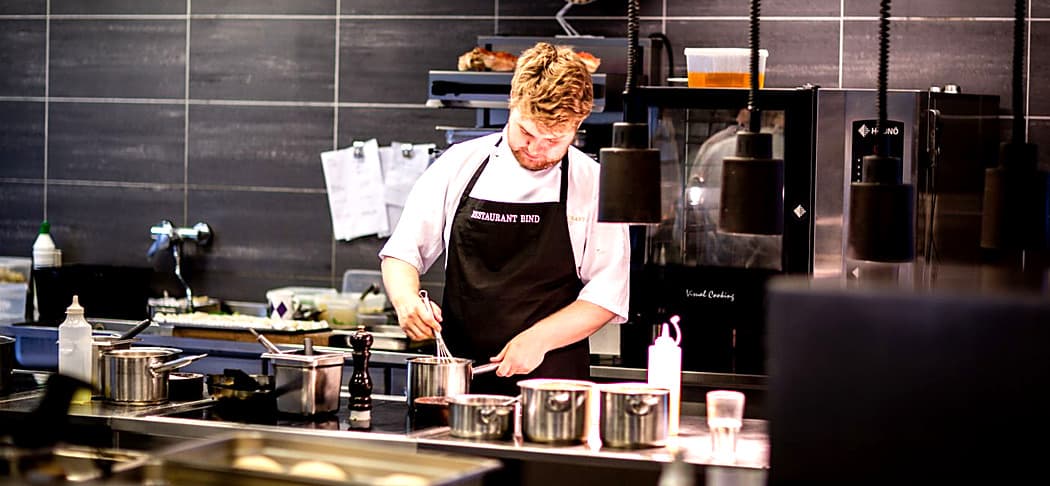
Forecasting that works with real kitchens
What we learned taking demand prediction to work in the field.
Read more
Find out how ready you are for your next audit
Thirty minutes with the engineers who would do the work, walked through your current posture. No obligation, no slide deck.